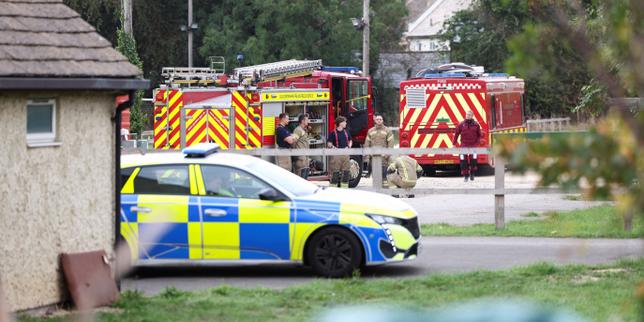
Security failures do not happen in a vacuum. When Donald Trump publicly declared that UK terror suspects aimed for maximum damage at a British military installation, the statement instantly reignited a contentious transatlantic debate over intelligence sharing, insider threats, and the vulnerability of joint operating bases. This specific incident involves individuals arrested under counter-terrorism legislation following intelligence pointing toward a targeted strike on critical aviation and defense infrastructure. But the soundbite from Washington obscures a much darker, structural reality: the modern military airbase, designed for rapid power projection, remains profoundly exposed to low-signature, high-consequence asymmetrical attacks.
We have been here before. Decades of counter-terrorism operations across Europe and North America have proven that security protocols are reactive, forged in the ashes of the last near-miss rather than the foresight of the next. To understand what actually happened at these UK facilities, one must look past the political posturing and examine the intersection of radicalization vectors, perimeter vulnerabilities, and the fragile dependencies of modern military logistics.
The Anatomy of the Threat Vector
Military installations like RAF Mildenhall and RAF Lakenheath in Suffolk are not merely hangars and runways. They are sprawling mini-cities housing nuclear-capable assets, intelligence-gathering platforms, and thousands of service personnel alongside civilian contractors. When a plot targets these locations, the objective is rarely straightforward destruction. It is psychological warfare wrapped in strategic disruption.
The primary vulnerability of any modern airbase is its supply chain and workforce integration. Modern defense installations rely heavily on local civilian contractors for base maintenance, catering, logistics, and IT infrastructure. This creates an administrative blind spot. A radicalized individual does not need to scale a perimeter fence with a rifle if they already hold a security badge, routine access codes, and knowledge of shift changes.
Intelligence agencies monitoring these networks have watched a tactical shift away from complex, highly coordinated multi-cell operations toward decentralized lone-wolf actions and small-cell radicalization. Individuals operating within low-tier support roles are groomed or self-radicalized via encrypted communication channels, turning their everyday proximity to high-value assets into an operational advantage. When political figures point to the ambition of causing "big damage," they are acknowledging a chilling mathematical reality: an insider with a rudimentary explosive device or access to critical fuel infrastructure can achieve a disproportionate strategic impact compared to an external assault force.
Intelligence Sharing and the Transatlantic Friction
Public commentary from American political leaders regarding British security operations often causes quiet friction within the corridors of MI5 and MI6. Joint counter-terrorism cooperation is historically robust at the tactical level, but strategic messaging frequently diverges.
When details of ongoing investigations are prematurely publicized or framed through a political lens, it complicates the delicate chain of evidence required for successful prosecution in British courts. UK counter-terrorism strategy traditionally favors prolonged surveillance, allowing law enforcement to map entire networks, identify financiers, and intercept communication lines before moving in for arrests. Premature disclosure can burn operational sources, tip off secondary suspects hiding across European borders, and force premature raids that yield lower evidentiary yields.
Furthermore, the UK threat level, managed by the Joint Terrorism Analysis Centre, operates on a complex matrix of domestic and international indicators. While the threat remains substantial, framing every thwarted plot through the lens of catastrophic intent risks creating a reactive cycle of public alarm. Analysts must balance transparency with operational security, ensuring that the public understands the nature of the risk without inducing panic or playing into the propaganda goals of extremist organizations.
The Hard Choices Facing Defense Infrastructure
Securing a sprawling military reservation against internal subversion is an administrative nightmare. Physical security upgrades—reinforced perimeters, biometric access controls, and advanced drone detection systems—are standard operating procedure. Yet, hardware cannot solve a human problem.
Screening processes for civilian contractors and local national employees undergo regular reviews, but background checks can only flag known associations or criminal records. They cannot accurately predict ideological drift, online radicalization, or psychological vulnerability. As counter-terrorism agencies adapt to encrypted messaging platforms and decentralized recruitment models, the traditional vetting model begins to fracture.
Defense planners are now forced to weigh the cost of hyper-vigilance against operational efficiency. Restricting contractor access, increasing surveillance on base personnel, and tightening international information-sharing protocols require significant financial investment and cultural shifts within military command structures. If every worker is treated as a potential insider threat, internal trust erodes, and mission capability slows down.
The thwarted plots against British airbases serve as a stark reminder that the post-9/11 security architecture is under constant strain. The threat has evolved from state-sponsored terrorism and hierarchical al-Qaeda cells to diffuse, ideological networks operating in the shadows of the digital economy. As long as vital military nodes remain integrated with civilian supply chains and local workforces, the friction between open society security and absolute defense will persist. The real danger is not just the bomb that might go off, but the quiet erosion of institutional resilience when every routine shift carries the weight of a potential catastrophe.