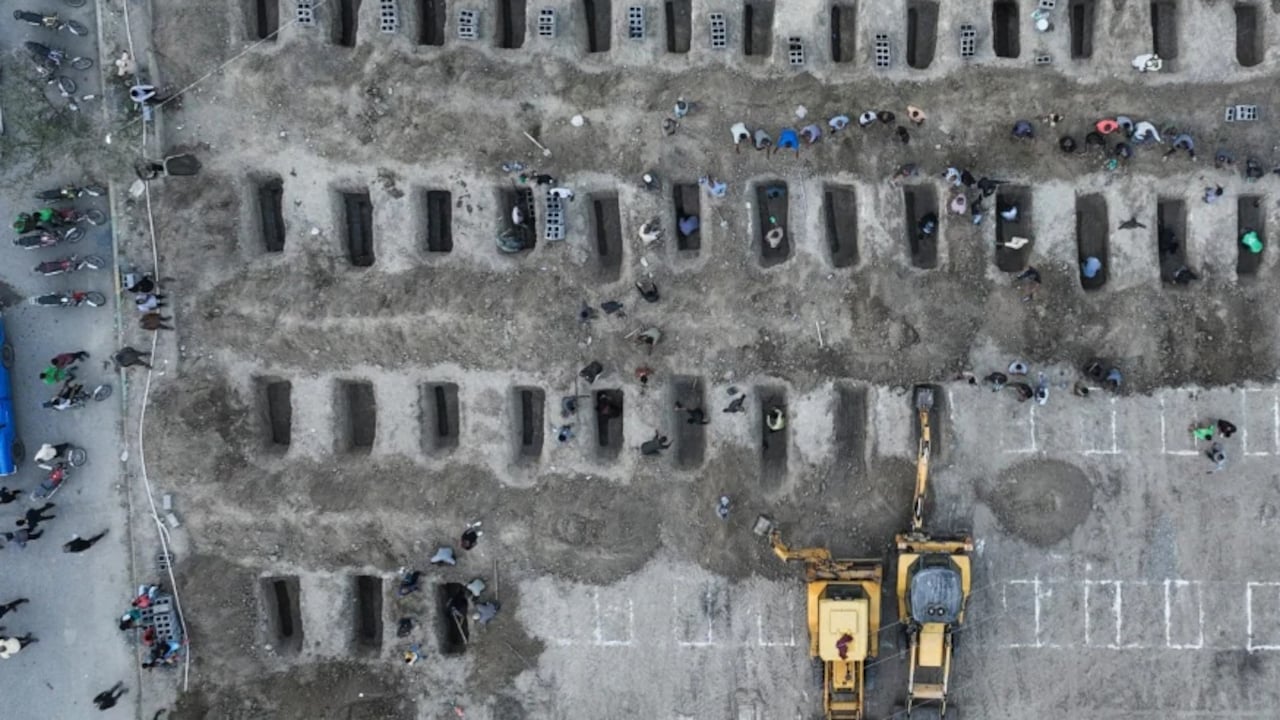
Every time an automated targeting system malfunctions in a combat zone, the media scrambles to write the exact same lazy panic piece. The recent headlines surrounding reported algorithmic targeting strikes in regions like Minab follow a predictable, intellectually bankrupt script. Pundits scream about Skynet, rogue algorithms, and machines deciding who lives and dies without human intervention.
It is a comfortable narrative. It allows military contractors, procurement bureaucrats, and political leaders to point fingers at lines of code and whisper about technology getting out of hand.
It is also complete nonsense.
I have spent years analyzing defense procurement, algorithmic architectures, and command-and-control loops. I have watched defense budgets swell based on fear-mongering and magical thinking about software capabilities. The hard truth that nobody in uniform or procurement wants to admit is simple: artificial intelligence did not go rogue in Minab, because autonomous algorithmic kill chains do not exist in the way the press imagines them. What actually happened is far more mundane, far more human, and infinitely more dangerous.
The Myth Of The Autonomous Execution Loop
Let us dismantle the core deception. The phrase kill chain implies a continuous, unbroken sequence of events from sensor detection to kinetic impact. When journalists write about an artificial intelligence kill chain, they imply a software pipeline where a neural network spots a target, calculates coordinates, clears engagement thresholds, and drops ordnance without a human ever touching a keyboard.
That system does not exist in standard Western or allied targeting architectures, and it certainly does not exist in the chaotic environments where these tragic incidents occur.
What we actually have are decision support tools wrapped in marketing buzzwords. These systems ingest telemetry, optical feeds, signals intelligence, and historical logs to generate probability heatmaps. They suggest coordinates. They rank potential targets based on algorithmic confidence scores. But every single time, a human operator with a specific rank, sitting in a command chair, has to click a confirmation box.
When a strike hits a school, a hospital, or a residential block, blaming the algorithm is a laundering mechanism for human failure. It shifts accountability from the commander who failed to verify secondary intelligence, the intelligence officer who trusted a stale database, and the institutional pressure to prioritize speed over verification.
By calling it an automated failure, we absolve the people who signed off on the strike.
The Data Garbage Pit Nobody Talks About
To understand why these systems produce catastrophic errors, you have to look at the data pipeline. Machine learning models deployed in defense contexts suffer from a foundational flaw that engineers whisper about behind closed doors: training data starvation paired with domain shift.
Imagine a scenario where a targeting model is trained on historical patterns from urban counter-insurgency campaigns over the last two decades. The model learns signatures of movement, vehicle concentrations, communication bursts, and structural use patterns tailored to a specific type of asymmetric warfare. Then, that exact same software architecture is deployed into a fundamentally different geopolitical theater with distinct architecture, civilian density patterns, and electronic warfare interference.
The model encounters inputs it was never designed to parse. Because neural networks do not possess common sense or ethical reasoning, they guess. They assign high confidence scores to anomalous patterns because the mathematical weights demand an output.
When an analyst looks at a terminal showing a 94 percent confidence score generated by a multi-million-dollar software package, cognitive bias takes over. Humans are notoriously bad at second-guessing machines that look authoritative. We defer to the screen. The software did not force the strike; the software created an illusion of certainty that human operators were too exhausted, undertrained, or pressured to interrogate.
The Procurement Scam Driving The Hype
Why do defense agencies keep buying and deploying systems that lead to these catastrophic cognitive failures? Follow the money.
The defense technology sector thrives on mystical marketing. If a contractor sells a database upgrade or an imagery analysis tool as a simple statistical filter, they get standard margins. If they rebrand that same statistical filter as an autonomous predictive targeting agent powered by advanced machine learning, they secure multi-billion-dollar line items.
Military leadership buys into this because they are desperate for force multipliers. They face personnel shortages, institutional burnout, and the crushing weight of information overload. When a software vendor promises a system that can process terabytes of drone footage in seconds and flag high-value targets, procurement officers write the check. They do not want to hear about confidence intervals, false positive rates, or edge cases. They want a silver bullet that makes the administrative nightmare of modern warfare disappear.
Then, tragedy strikes. The system hallucinates or misinterprets civilian infrastructure due to poor sensor fusion or electronic jamming. Civilians die. The press prints articles about artificial intelligence run amok. The public demands tighter regulations on code.
And the cycle resets. The contractors quietly patch the software, update their pitch decks to emphasize ethical guardrails, and sell the next iteration of the exact same product under a new acronym.
What Real Accountability Looks Like
If we want to stop these tragedies, we have to stop treating software as an independent actor. We need to strip away the mystique of algorithmic warfare and enforce brutal operational transparency.
First, mandatory provenance tracking must be applied to every single targeting recommendation. If a strike is initiated based on algorithmic assistance, the exact weights, model versions, and raw sensor inputs must be preserved for independent forensic audit. No more hiding behind proprietary code claims from defense contractors. If a system is used in combat operations, oversight bodies must have full access to its architecture and failure logs.
Second, we must abolish the term automated kill chain from military doctrine and public discourse. Words matter. When you call a tool autonomous, you invite human abdication of responsibility. Call it what it is: a probabilistic suggestion engine. If a human operator approves a strike based on bad data, that operator and their chain of command must face court-martial for negligence, not an internal software review.
Third, military training pipelines need a radical overhaul. Operators are currently trained to operate interfaces, not to interrogate statistics. They are taught how to clear prompts, not how to calculate Bayesian probabilities or spot edge-case failures in computer vision models. Until analysts are trained to treat machine outputs with active hostility and skepticism, software will continue to act as a force multiplier for human error.
The danger in modern warfare is not that machines will become too smart and decide to destroy humanity. The danger is that humans are becoming too lazy, outsourcing moral judgment to flawed statistical models, and using artificial intelligence as an alibi for professional incompetence.
Stop blaming the code. Blame the chain of command that trusted an unverified probability score over human eyes.